
PHP2Shell is the name given to two newly disclosed critical vulnerabilities in PHP, CVE-2026-109618 and CVE-2026-109619. Both carry a severity score of 9.2/10 and can potentially allow an attacker to execute code on an affected server without authentication.
Why does this matter? Because the vulnerability sits in PHP itself, not simply in a particular application or plugin. PHP underpins nearly 70% of websites worldwide, business applications, hosting environments and even some vendor products and appliances.
Think of it this way: this isn’t a vulnerability in something attached to the engine. It’s in the engine.
The bigger story is speed
What makes PHP2Shell particularly interesting is what happened before the vulnerability became public.
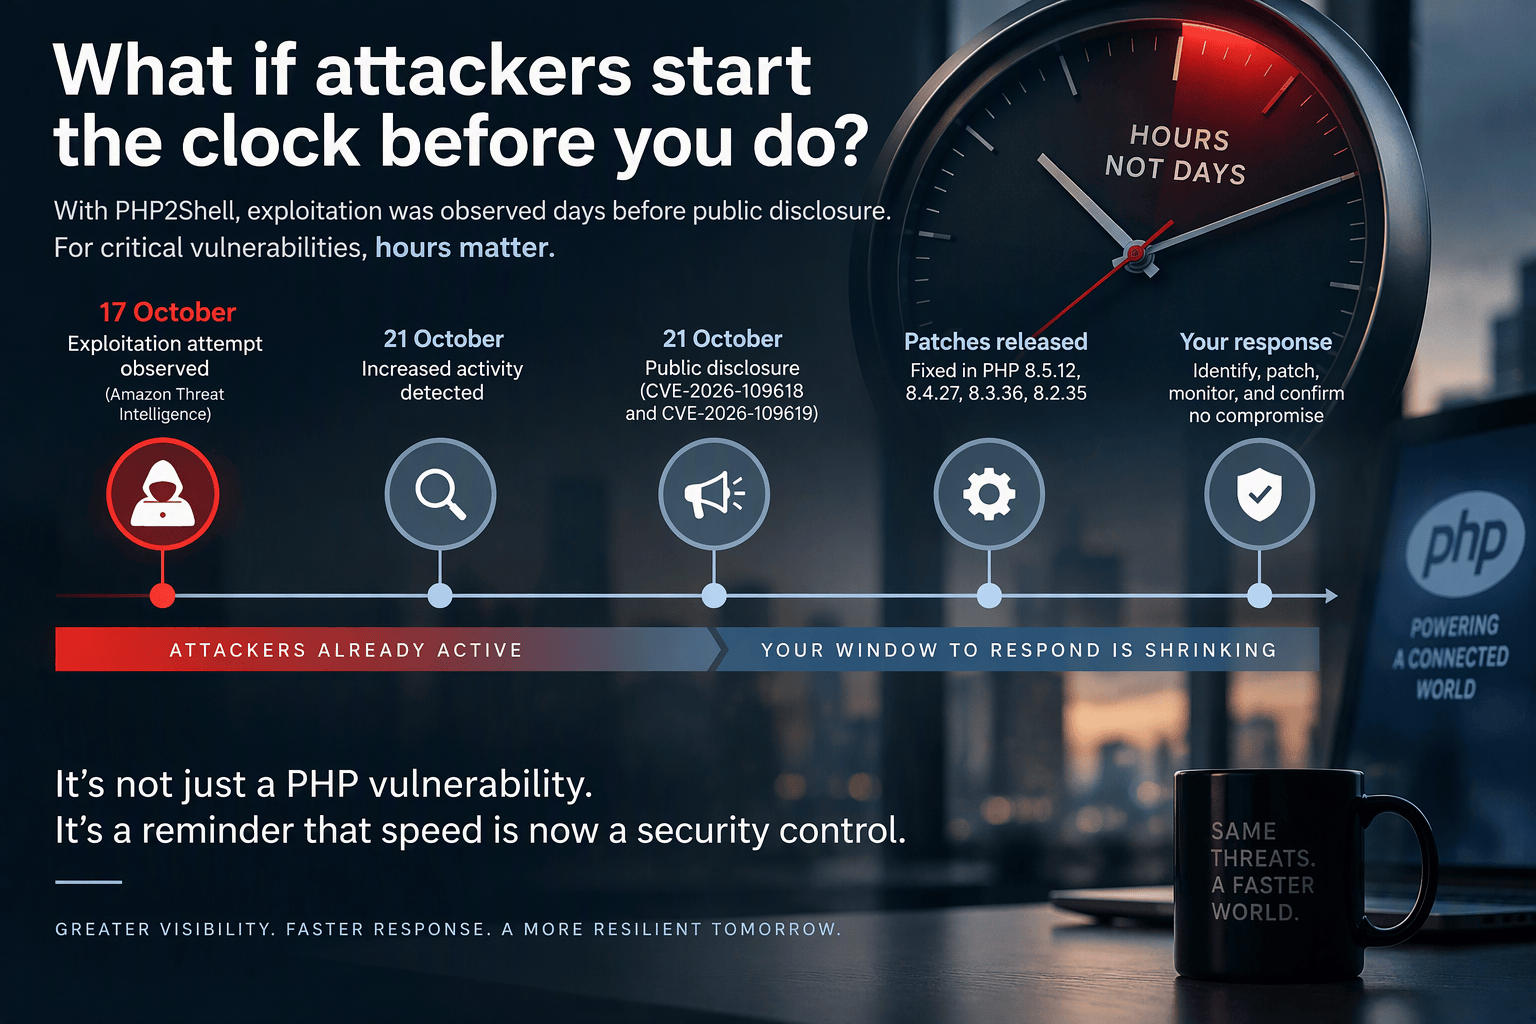
Amazon Threat Intelligence reports that it detected an exploitation attempt on 17 October, four days before public disclosure. After disclosure, additional proof-of-concept exploits appeared within hours and were quickly observed against its sensors.
That challenges a long-standing assumption in vulnerability management: that defenders have a reasonable window between disclosure and exploitation.
Increasingly, they don’t.
Amazon Threat Intelligence also points to AI-assisted vulnerability analysis as one reason this window is shrinking. Turning newly disclosed technical information into a working exploit is becoming faster and accessible to more actors
For critical internet-facing vulnerabilities, days may already be the wrong unit of measurement. Hours matter.
What should organisations do now?
The immediate response is straightforward:
- Know your exposure. Identify where PHP exists, including less obvious places such as legacy applications, appliances and vendor products. [servicenow.com], [github.com]
- Prioritise internet-facing systems. Patch supported PHP environments immediately and isolate vulnerable systems that cannot yet be updated. [aws.amazon.com], [servicenow.com]
- Look backwards, not only forwards. Given the activity observed before disclosure, organisations should check for signs of compromise from at least 17 October, rather than assuming the risk began when the advisory appeared. [aws.amazon.com]
- Challenge legacy technology. Unsupported runtimes create exposure precisely when organisations have the least time to respond. [tuxcare.com], [github.com]
The leadership takeaway in the AI world
PHP2Shell will be patched. Another critical vulnerability will eventually replace it.
The more important question for CIOs and CISOs is:
If a critical vulnerability emerged tomorrow, could we identify our exposure, determine ownership and act within hours?
If answering that question requires spreadsheets, manual discovery and emails across application teams, the real vulnerability may not be the software.
It may be the operating model around it.
And perhaps that’s the bigger shift AI is creating in cybersecurity: attackers are accelerating, so visibility and response speed increasingly become security controls in their own right.
